


Connect repository Select a repository and branch to audit.
Repository
Select a repository sentinel-labs / defi Public
Connect your repositories
Choose a repository and branch to audit.

 Solace
Professional-grade smart contract security without the traditional audit process, long timelines, or five-figure engagement, built for teams that want answers faster.

 and Solana / Anchor



 Synergy™

 Horizon™

 Catalyst™

 Phoenix™

 Pulse™

 Solaris™

 Aurora™

 How it works?
Pay per audit. No subscription. No plans. No sales call.
Choose a repository and branch to audit.
Pick exactly what you want reviewed.
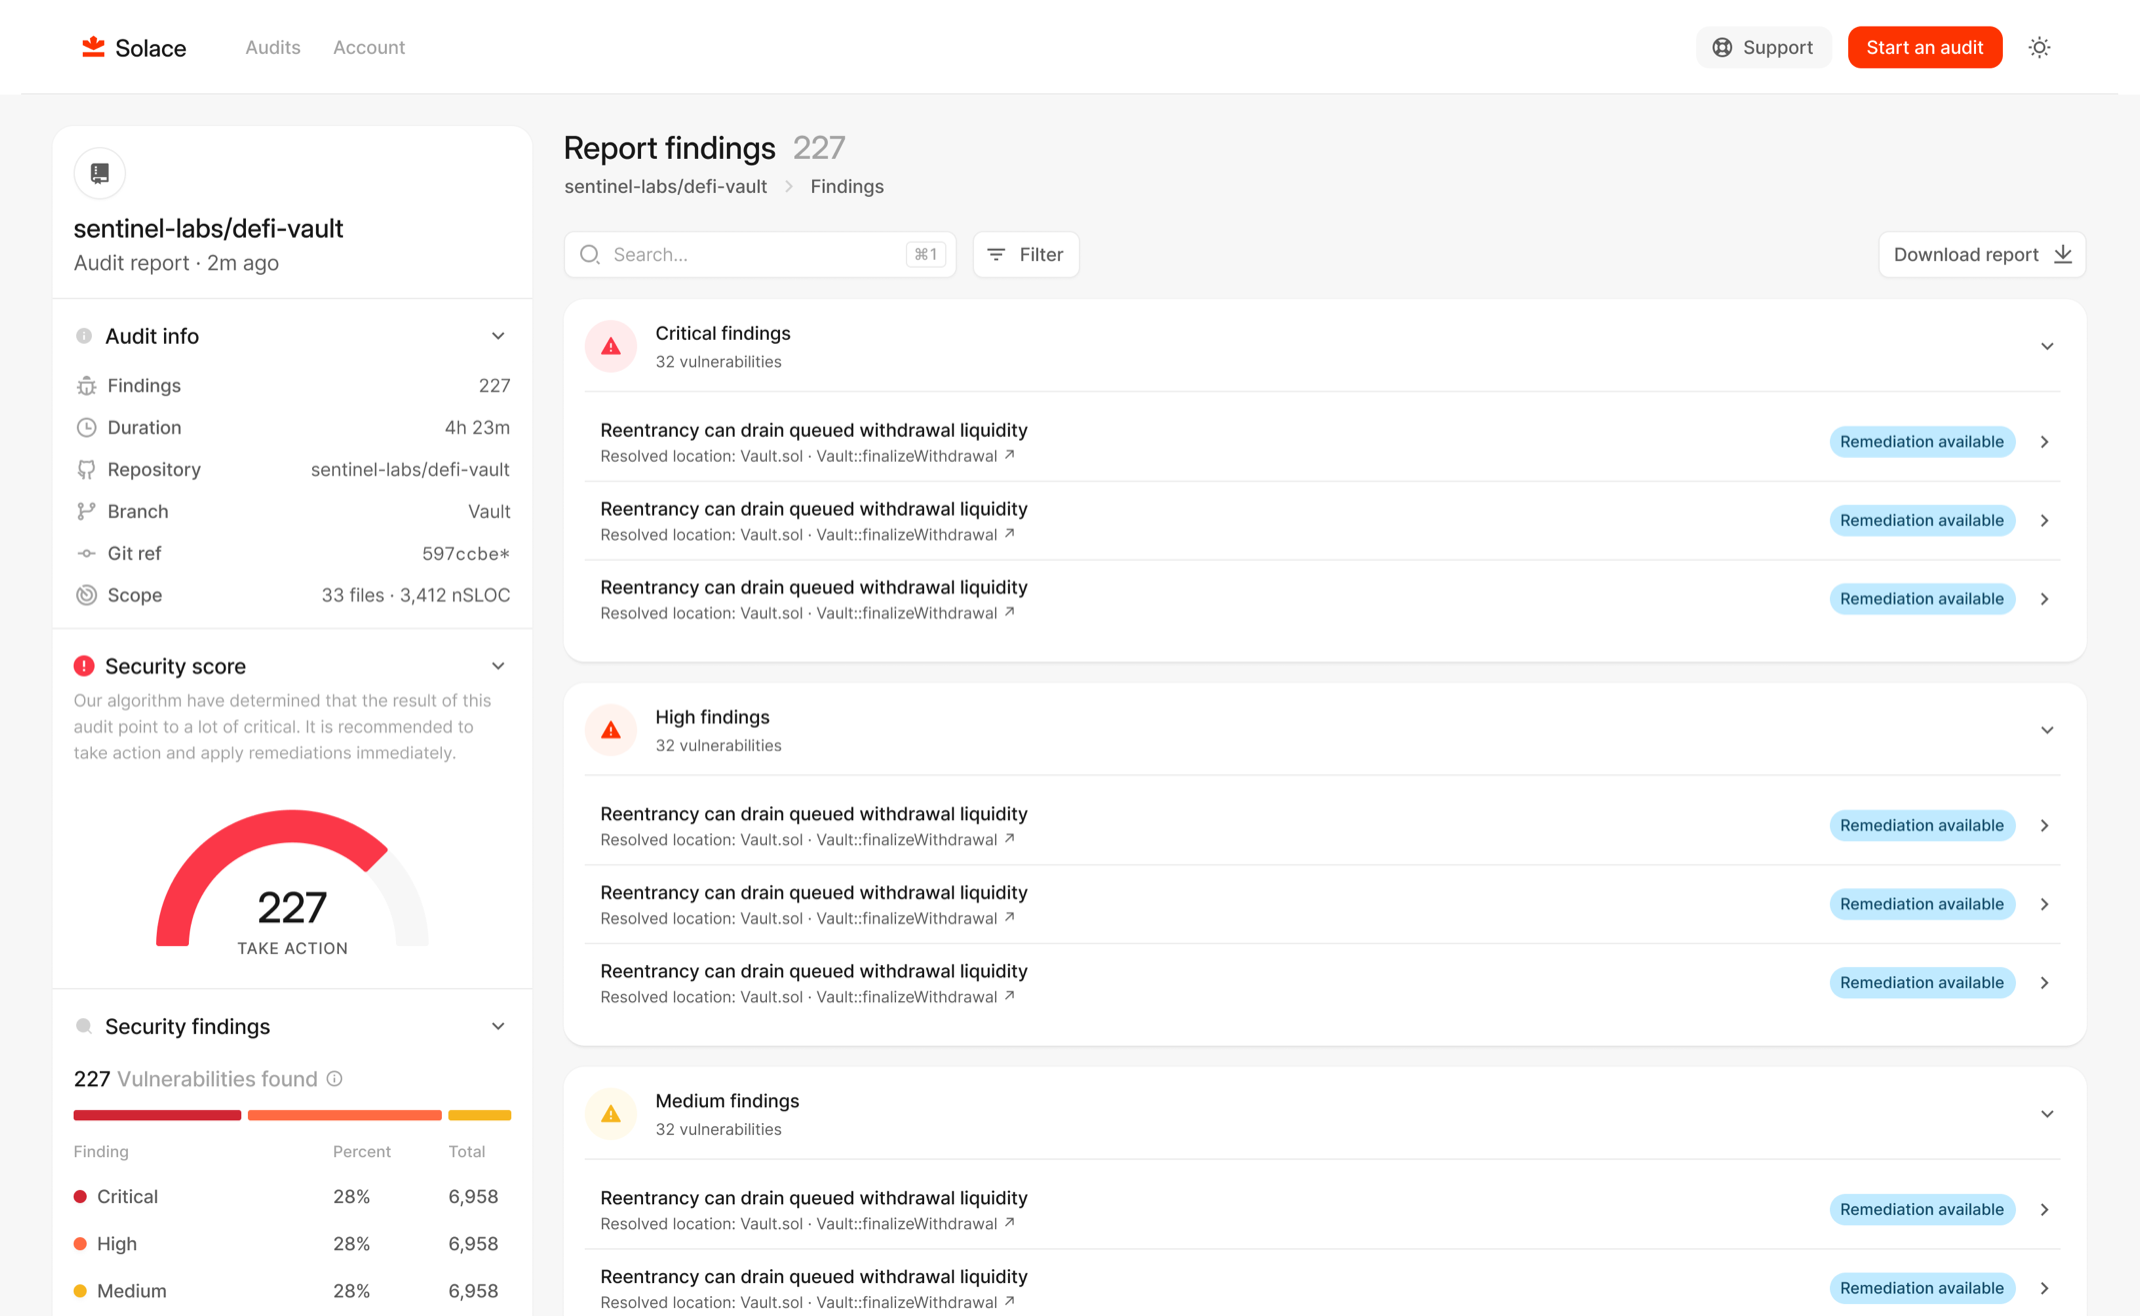
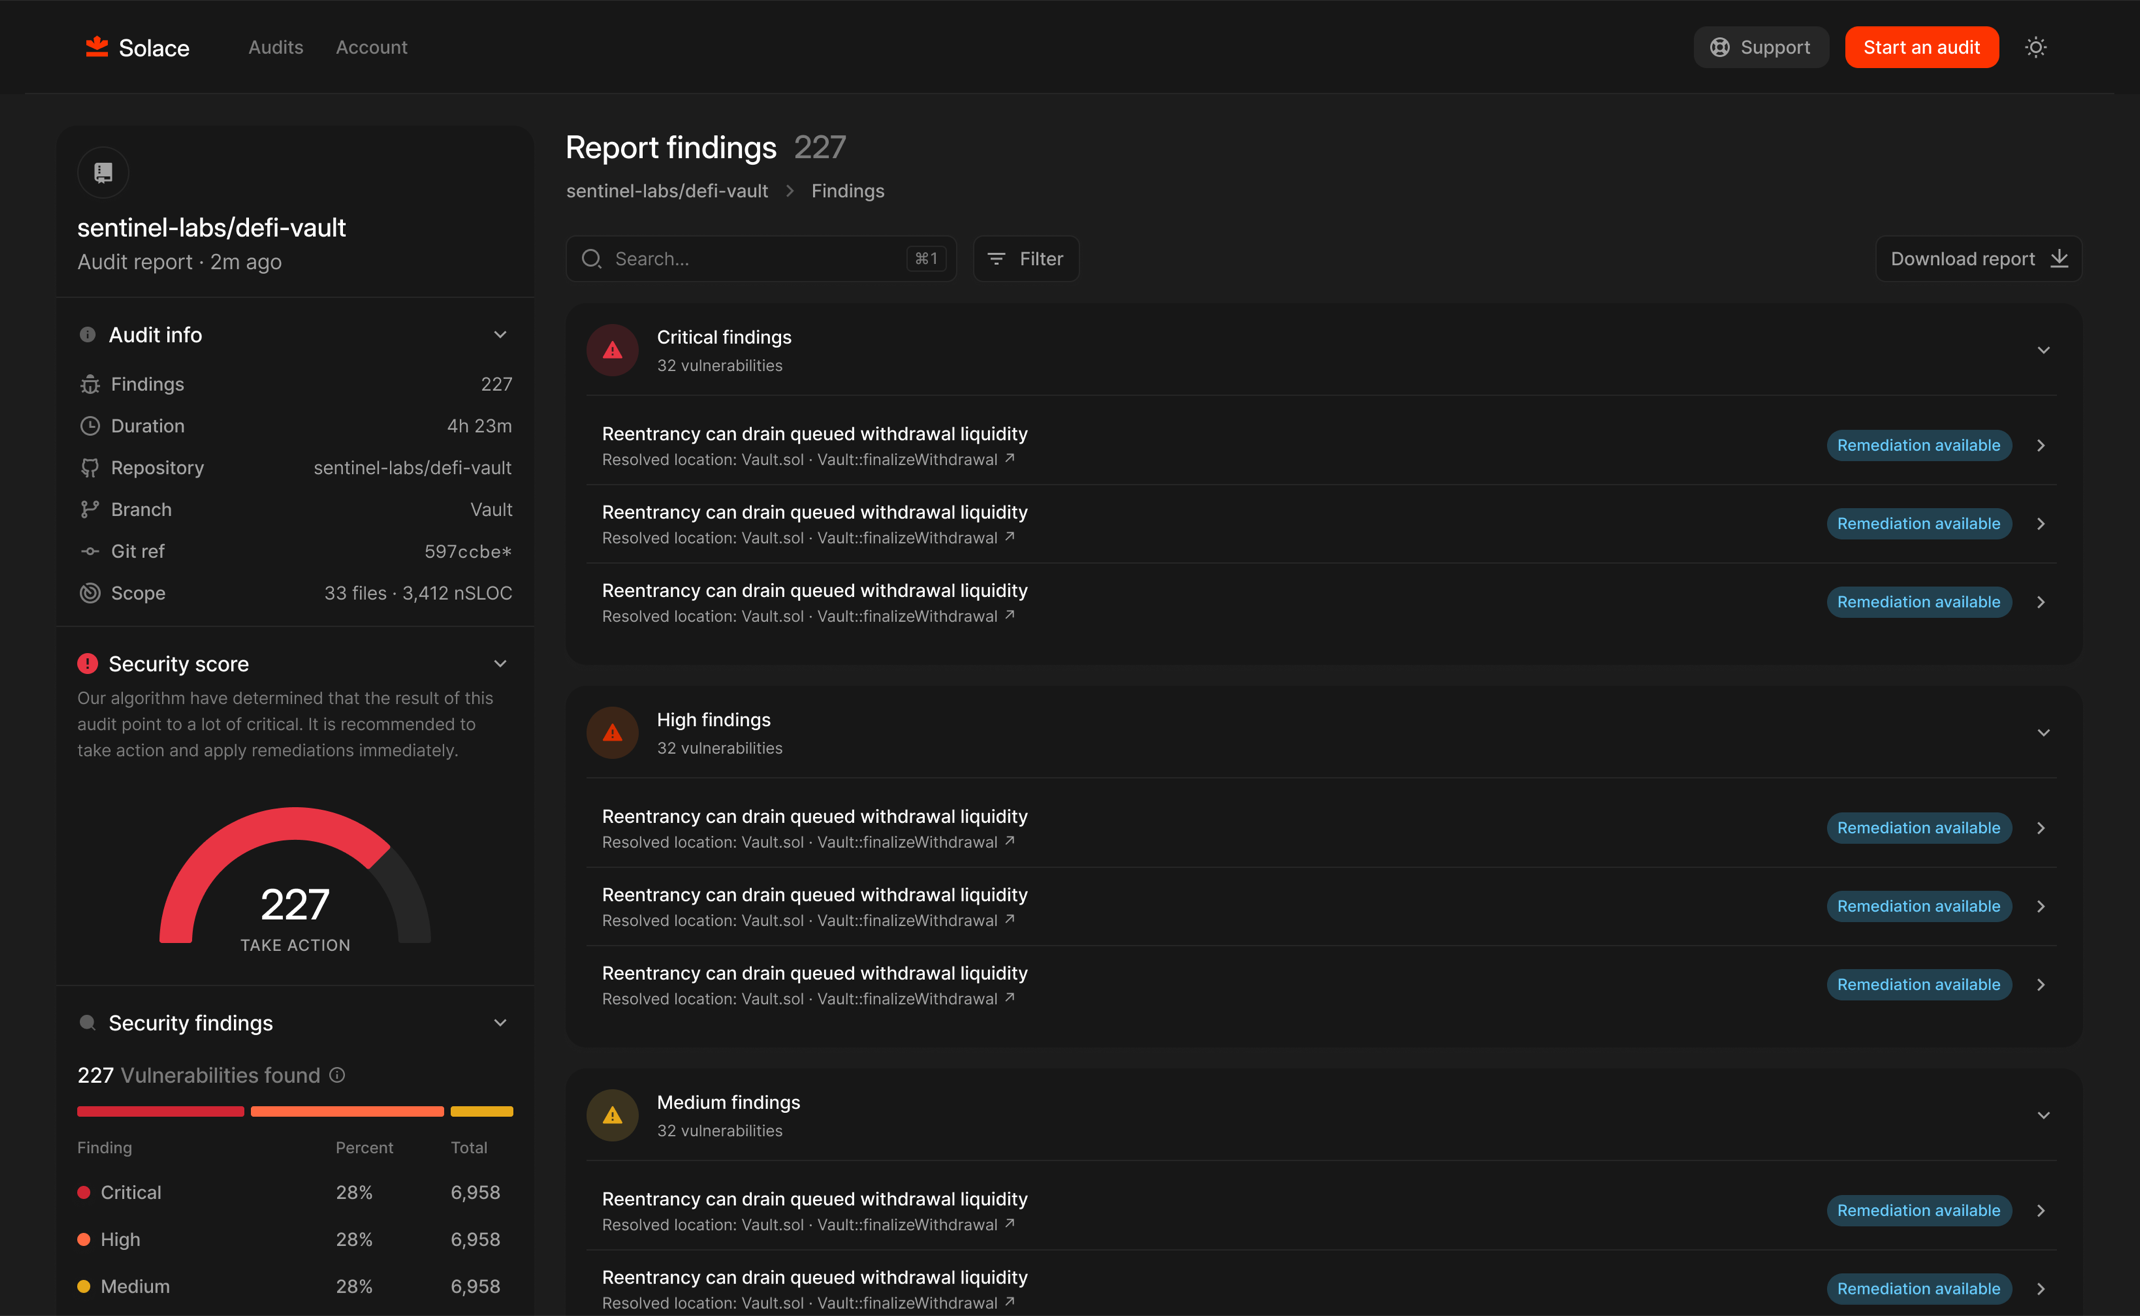
Detailed findings, ready in a few hours.

 Performance metrics
Solace strips away the coordination, quoting, and scheduling around an audit, so you can go from repository to security report with far less friction.
View sample reportMore parallel reviewers
Faster turnaround at 6,000 nSLOC
Median findings per audit scan
Cheaper starting cost vs traditional audits

 Security
Solace is built on security tooling and methodology developed through real smart contract audit work.


Maps the codebase and attack surface before hunting begins.


Specialized security agents review your code in parallel.


Potential issues are verified and severity-calibrated before reporting.


Critical paths are tested with PoCs and composite exploit reasoning.


Uses your docs, trust model, and invariants to reduce false positives.


Structured findings with impact, mitigations, scope, and a shareable PDF.

 Trusted by top Web3 companies
See how teams use Solace to surface vulnerabilities earlier, move faster, and strengthen their security process before deployment.

 Synergy™

 Apex™

 Horizon™

 Catalyst™

 Phoenix™

 Pulse™
Everything we needed was already built in reporting, automation, integrations.

 Apex™
Everything we needed was already built in reporting, automation, integrations.

 Catalyst™

 Pricing
Pay per audit. No subscription. No plans. No sales call.
A focused smart contract review to understand and remediate findings.


 Up to 6,000 nSLOC Multi-agent security review Validated, severity-ranked findings Proofs of concept where applicable Recommended mitigations Web report + downloadable PDF
 — trusted by 250+ leading Web3 companies
For larger than 6k nSLOC or more complex scopes requiring hands-on review.
Review by lead security researchers Detailed PoCs and remediation guidance Direct collaboration with your eng team Final report with mitigations verified

Connect your repository and start your audit
in under 5 minutes.

 Frequently asked questions
Answers on pricing, privacy, turnaround, and coverage.
A Complete Audit costs $200 for one repository commit and one fixed Scope.
Timing depends on queue depth and repository complexity. The status page shows each review stage as it completes.
Each audit supports up to 6,000 nSLOC. Documentation does not count toward the limit.
Solace supports Solidity on listed EVM chains, Solana programs, and supported Substrate/FRAME targets. Choose one deployment chain per Scan. Shared or ambiguous files require a Scope review; unlisted targets and other languages are not supported.
Yes. Grant Solace access only to the repository you want reviewed; GitHub sign-in alone does not grant code access.
No. Repository code is used only to perform the requested review.
A failure does not consume your Credit. Repository problems are explained so you can retry, and Solace-side failures leave the Credit intact.
Looking for something else? support@cyfrin.io


Get a professional-grade security review in just a few hours.


